

Secrets
A secret is an API key or token your scripts use, such as the admin
key that lets Support’s unlock-account script call your app’s admin
API. Reminix keeps it so the code doesn’t have to.
- Write-only. Once you save a value, nobody can see it again in the app, the API, the CLI or through an agent. To rotate it, save a new value.
- Encrypted at rest. Reminix encrypts each value with a key for its workspace.
- Sent only to its hosts. Each value lists the hosts Reminix may
send it to, such as
api.yourapp.com. Reminix adds the value to a script’s requests to those hosts and to nothing else, whatever the code says. A script you let read the value can send it to any host the script’s version allows. - One value per environment. A run uses the value for its own environment, such as a test key in staging and the live key in production.
- Not readable by code. The exception is a secret where you turn
on “Let scripts read it as an environment variable” (
allowEnvVar). - Kept out of output and logs. If a run prints a secret value it
had access to, Reminix replaces it with
[secret]in the run’s output, log and error. Reminix also catches the value when it’s base64- or URL-encoded. Reminix doesn’t scan files a run saves, so never write a secret to/saved.
Workspace owners and admins save, rotate and delete secrets. Members see
each secret’s name and hosts, but never its value. They need the name
and hosts to write a reminix.json.
Saving one
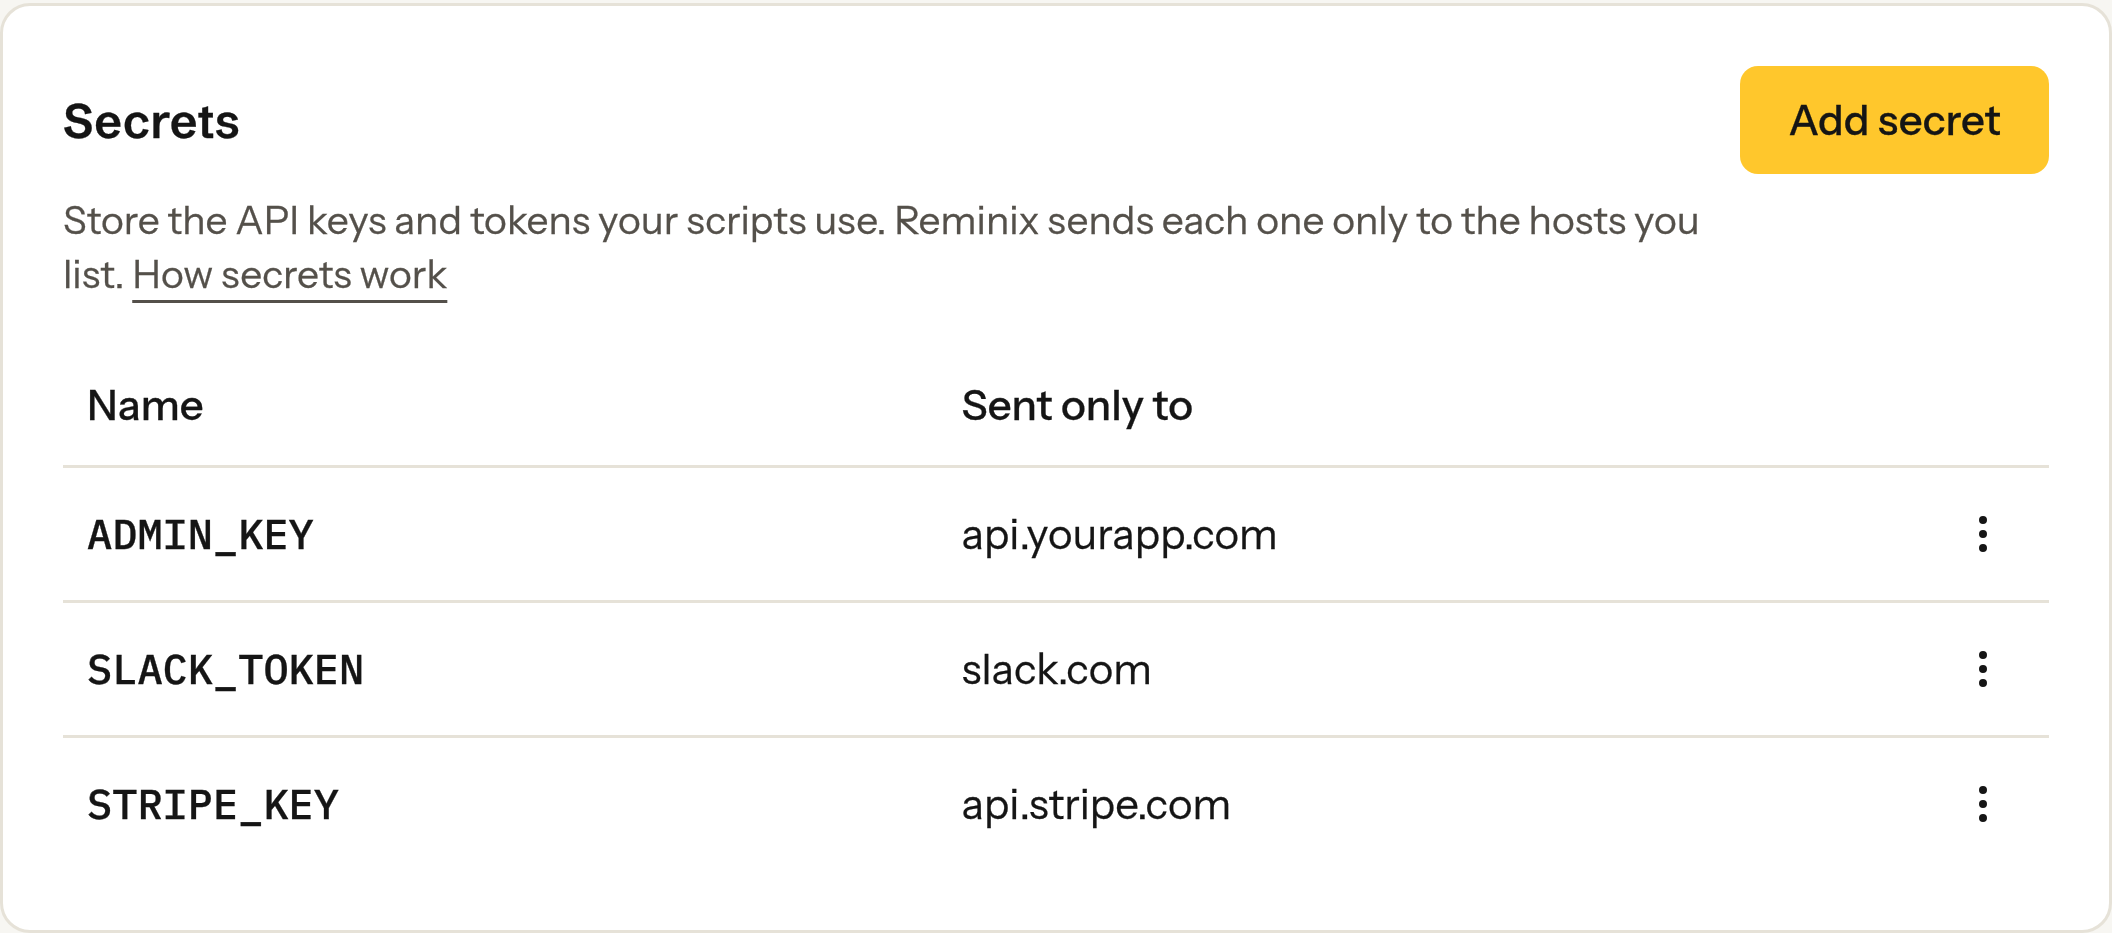
Section titled “Saving one”In the app, go to Settings → Scripts → Add secret. If your workspace has more than one environment, the page is a grid with a column for each one. Use Set to add a missing value. A saved value’s ⋯ menu shows when a run last used it, and it has Rotate and Remove.
With five environments or more, each secret is one row that says where it has a value, as in “Set in 3 of 10”. Its Environments button lists every environment with a checkbox. Tick one to give the secret a value there, or untick it to remove that value.
From the CLI or your code, Reminix saves the secret in the environment
you act in. It’s the workspace’s default environment unless you name
another. A key or token needs secrets:write:
import { createClient } from "@reminix/sdk";
const reminix = createClient({ environment: "staging" });
const secret = await reminix.secrets.set("ADMIN_KEY", {  value: process.env.STAGING_ADMIN_KEY!,  hosts: ["api.staging.yourapp.com"],});console.log(secret);
import os
from reminix import Reminix
reminix = Reminix(environment="staging")
secret = reminix.secrets.set( "ADMIN_KEY", value=os.environ["STAGING_ADMIN_KEY"], hosts=["api.staging.yourapp.com"],)print(secret)The CLI reads the value from standard input, never from an argument, because an argument would end up in your shell history. The command says which environment it saved to:
printf %s "$ADMIN_KEY" | reminix secrets set ADMIN_KEY --hosts api.yourapp.comprintf %s "$STAGING_ADMIN_KEY" | reminix secrets set ADMIN_KEY \ --hosts api.staging.yourapp.com --environment stagingcurl -X PUT https://api.reminix.com/v1/secrets/ADMIN_KEY \ -H "Authorization: Bearer $REMINIX_API_KEY" \ -H "X-Environment: staging" \ -H "Content-Type: application/json" \ -d '{ "value": "…", "hosts": ["api.staging.yourapp.com"] }'reminix secrets list shows each secret’s name and the hosts it may go
to in each environment. It never shows a value. To remove one
environment’s value:
reminix secret-values delete ADMIN_KEY stagingreminix secrets delete ADMIN_KEY deletes the secret everywhere. The
same operations are under Secrets in the
API reference. Agents can list secrets but never save or delete them. An
agent that needs a secret asks you to add it.
Using one
Section titled “Using one”A script declares the secrets it uses in its reminix.json. See
Scripts → Calling APIs. A run uses the
value for its own environment, and only for the hosts that value
allows. If the environment has no value, the run fails before it
starts. Reminix never borrows another environment’s value. After a
rotation, the next run uses the new value.